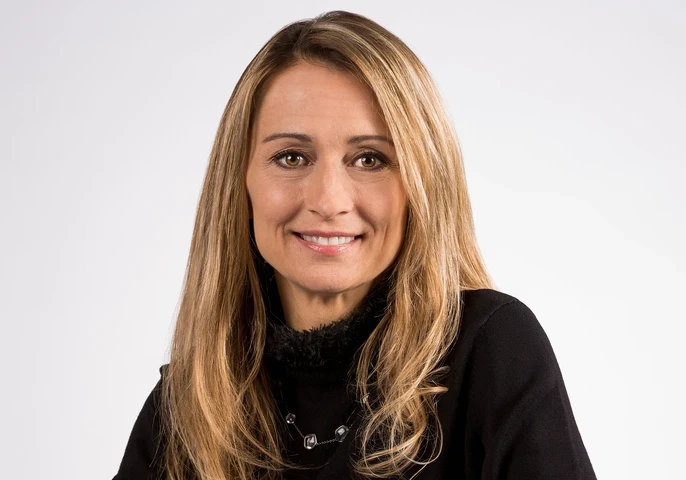
After four decades working across cybersecurity, from CISO roles in the public and private sectors to industry analysis anresearch leadership, Wendy Nather has developed a perspective that challenges some of the technology industry's most established assumptions.
Rather than focusing solely on the latest developments or emerging technologies, Nather is interested in the wider forces shaping how organisations approach security: from financial and operational constraints to the human and political dynamics that influence decision-making.
One concept that has remained central to her work is the security poverty line, which explores why many organisations struggle to achieve the level of cybersecurity that conventional industry advice suggests they should. It's a perspective that also informs her thinking on AI, the future of enterprise technology and the importance of questioning long-standing assumptions.

I recently sat down with Wendy to discuss her career, the realities of defending organisations, the industry's changing approach to AI and why cybersecurity needs a more realistic understanding of the challenges businesses face.
A Career Built on Challenging Assumptions
Nather's career has taken her through several different areas of the cybersecurity industry. Having worked as a CISO in both public and private sectors, as well as an industry analyst and research director, she has developed experience across a broad range of technology and security disciplines.
Rather than identifying with one particular specialism, she values the opportunity to explore new areas and understand different environments.
"I've been a CISO in the public and private sectors, and I've also been an industry analyst and a research director in various capacities. I'm one of those people who doesn't actually specialise, since as a CISO and analyst I've had to work in areas across the board. When I get the opportunity to research something new, or try something in a new environment, I really enjoy it."
That broad perspective is reflected in one of the themes she has spent considerable time exploring: the security poverty line.
Understanding the Security Poverty Line
A recurring frustration for Nather is the tendency to assume that organisations struggling with cybersecurity simply aren't doing enough. In reality, she argues, the resources and capabilities needed to implement effective security are not equally available to everyone.
Her concept of the "security poverty line" describes the gap between what organisations are expected to achieve and what they can realistically afford or implement.
"There are a few themes that I get passionate about. One is the concept that I call the "security poverty line," which describes why it's not as easy for most organisations to secure themselves as conventional wisdom says they should. Budget is one problem, of course, but they also struggle with expertise, capability, and influence. And it drives me crazy when people who have never experienced security from the defense side make all kinds of generalizations about these organizations being unaware, or stupid, or lazy, or malicious. There are a lot of technical, economic, political, and cultural dynamics in play, just as there are with regular poverty."
It's a challenge to the way the industry talks about cybersecurity maturity. Advice about security fundamentals can sound straightforward, but implementing those recommendations requires resources, expertise and organisational support that many security teams simply don't have.
Nather has also questioned whether the industry truly understands the cost of effective security in the first place. Her other work explores the need to democratise security, the chemistry of data, and the human cost when technology doesn't support delegation.
"I've talked about other issues as well, such as the fact that we still can't really say how much effective security costs, so we don't even know whether it's truly affordable in its current form and practice. I've given talks about democratizing security, analyzing the chemistry of data, and the human cost when technology doesn't support things like delegation."
This broader interest in the practical realities of security runs through much of her work, including the need to make security more accessible and to understand the human consequences when technology fails to support the people using it.
Gender Equality and Moving Beyond Gatekeeping
Having entered the technology industry around four decades ago, Nather has witnessed considerable changes in representation and leadership.
She is encouraged by the growing diversity of people taking on influential roles, but believes the industry still has to contend with forms of gatekeeping that can limit who is considered legitimate within technical communities.
"When I started in the field 40 years ago, it was very rare to encounter another woman. Today I'm delighted to see a huge influx of people of various genders taking up the reins and leading the industry. Of course, there are still holdouts who believe that if you're not doing technology the way that they are, you're not legitimate. That kind of gatekeeping rears its head every so often, in groups who are used to being the "wizards" and controlling the knowledge, and the best response in my opinion is just to laugh at them and go back to what you were doing. I hope we will get to the point where it doesn't matter what gender someone is, or whether they've transitioned, because gender-based hierarchies will no longer exist. But that's a problem for the whole society, not just the tech industry."
For Nather, the issue extends beyond representation within technology companies. It also concerns the attitudes and hierarchies that determine who gets to participate, contribute and be recognised as an expert.
Her advice to women building careers in enterprise technology follows a similar philosophy: avoid being restricted to one narrow area unless it is genuinely where your interests lie.
"Don't let yourself get pigeonholed, or locked in for your whole career into something narrow, unless you truly enjoy it. The high-level principles and concepts that we work with are ones that anyone can grasp; you don't need to have fifteen certifications. And because technology is changing so swiftly, every day we have to figure out new ways to keep pace with the developments, so you're really not behind anyone else. We're all at the same starting line every morning."
It's a reminder that experience and technical knowledge are not necessarily defined by the number of certifications someone holds or how long they have worked within one particular discipline. In an industry that changes constantly, the ability to keep learning and adapt remains essential.
AI, Bias and the Problem With Repeating the Past
Few developments have attracted as much attention as artificial intelligence, but Nather's perspective is less focused on its capabilities and more concerned with the assumptions embedded in the systems being built.
When asked whether AI could create a more inclusive technology industry or reinforce existing inequalities, she points to the data and assumptions that underpin the technology.
"Our training data is no different from the assumptions, biases and misconceptions that always go into the software we create. Just because it's probabilistic in nature doesn't mean it isn't guided by its model. So no, I don't think having the same people who wrote the previous software working on AI now will produce different results. The past is not the best source of learning data when the mission is to "do more of it.""
Her concern is that introducing a new technology does not automatically mean changing the thinking behind it. If the same assumptions and perspectives continue to shape the development process, AI risks reproducing the same problems in a different form.
It's a particularly relevant challenge as organisations increasingly integrate AI into business processes and decision-making. The technology may be new, but the data, people and institutional structures behind it are not necessarily any different.
The AI Conversation: From Gold Rush to Reality Check
When asked which technology trend is receiving the most attention, Nather is quick to acknowledge the obvious answer. However, what interests her most is not simply the technology itself, but the reaction it has generated across organisations and society.
"This is a trick question, right? (LOL.) If I didn't say "AI," I'd be accused of living on a desert island. I've never seen a technological development before that immediately generated so much division in the population it's supposed to serve. I've never seen new technology that came with top-down management pressure and threats. The financial picture associated with AI is baffling. So regardless of the technical validity or problems with AI, I'm more bemused by and interested in the sociology."
That focus on the social and organisational implications of AI is also reflected in how she sees conversations evolving.
The initial excitement surrounding AI is increasingly giving way to more difficult questions about liability, risk, costs and the concentration of power among a relatively small number of providers.
"I'm hearing a lot more conversations these days that are less about the original gold rush and more about the Finding Out phase of the journey. Discussions about liability that have been prompted by the "rogue AI" security breaches; warnings of concentrated risk in the small number of AI providers and hyperscalers; the rapid development of tooling to monitor and enforce token-usage charges; and the continued pushback on data center construction. I suspect within the next year or two we'll start to see conversations about how to unwind an organization's current AI investment, just as we see some businesses quietly migrating back from the cloud to on-premises infrastructure."
Her observations point to a more complicated phase of enterprise AI adoption. As organisations move beyond experimentation, they must contend with the financial and operational consequences of the technology, alongside questions about accountability and dependency on external providers.
For Nather, the next stage of the conversation may involve not just how organisations adopt AI, but whether they ultimately decide to reverse or restructure some of those investments.
Cybersecurity's Fundamentals Still Need Attention
While AI dominates industry discussions, Nather is keen to highlight a more persistent challenge: cybercrime continues, often enabled by security weaknesses that organisations have struggled to address for years.
The industry regularly refers to the importance of getting the basics right. But describing something as fundamental does not make it straightforward to implement.
"While we are distracted by AI, cybercrime continues, and a lot of it is enabled by security issues we haven't been able to address. We always talk about "the basics," but just because they're basic doesn't mean they're easy to implement. And if we've been trying and saying the same things for decades without getting any closer to improvement, then we need to question all our assumptions and dig deeper."
This connects directly to her thinking around the security poverty line. Organisations cannot simply be expected to implement every recommended security control without considering the financial, technical and organisational barriers they face.
It also raises a broader question about the industry's approach to persistent security problems. If the same recommendations have been repeated for decades without delivering the improvements expected, perhaps the assumptions behind those recommendations need to be examined more closely.
Digital Sovereignty and the Next Enterprise Technology Shift
Beyond AI, Nather sees the potential for another significant shift in how enterprise technology is distributed and controlled.
Over the decades, organisations have moved between localised and centralised infrastructure, with changes in computing power and network bandwidth influencing where technology and resources are located.
She believes geopolitics could now become a more significant factor in determining the next direction.
"Other than the obvious trend (see below), I'm not currently seeing much in the way of shifts. Over the decades, we've swung from localized and centralized to distributed technology and then back again, as computing power and network bandwidth variously leapfrog each other in capacity. I think we may soon see another swing towards localization or even balkanization. This time it won't necessarily be technology driving it; it'll be today's geopolitics and the resulting talk of digital sovereignty."
The idea of digital sovereignty introduces a different consideration into infrastructure decisions. Rather than being driven exclusively by technical capabilities or cost, organisations may increasingly need to consider national interests, geopolitical relationships and where their data and systems are controlled.
It is another example of how enterprise technology cannot be understood in isolation from the wider economic and political environment.
Can Anyone Really Predict the Next Era of Enterprise Technology?
When it comes to predicting what will define the next era of enterprise technology, Nather is refreshingly sceptical.
Rather than offering a definitive forecast, she questions the industry's tendency to package technological developments into sweeping predictions and new frameworks.
"Your guess is as good as mine! I've learned over time that you cannot predict where enterprise technology is going to go. I can only say that it will probably involve new "frameworks," maybe a "paradigm" or two, and the defense and financial services sectors will lead the way as per usual. We'll hear about the next era at the biggest conferences, while my dentist's office is going to trundle on with the legacy equipment and services it has today, not caring very much about what gets tech geeks excited."
It's a fitting conclusion to a conversation that repeatedly challenges the gap between industry narratives and the realities of implementation.
From the security poverty line to AI adoption, Nather's perspective is grounded in the belief that technology does not exist in a vacuum. Financial constraints, organisational structures, politics, culture and the people responsible for making systems work all influence what businesses can realistically achieve.
Perhaps the most important takeaway is that the industry needs to become better at questioning its own assumptions. New technology may capture the headlines, but understanding the circumstances in which it is adopted, and the people expected to make it work, remains just as important.
Comments ( 0 )